
If you're searching for birdeye login, you're probably trying to do one of two things right now. Get into the dashboard fast so you can answer reviews, update listings, and keep locations moving, or fix an access problem that's blocking your team from doing that work. That matters because the faster your team can respond and maintain accurate profiles in [City] or a “dentist near me” search in [Neighborhood], the better your odds of turning visibility into calls, messages, bookings, and tours.
For single-location owners, login is simple. For multi-location operators, franchises, and regional teams, login is really access management. The difference between those two is where most friction starts.
Table of Contents
- Why Your Birdeye Login Is Your Business's Front Door
- How to Access Your Birdeye Account
- Troubleshooting Common Birdeye Login Issues
- Admin Tips for Managing Team Access and Permissions
- Key Templates and Scripts to Use After You Log In
- Measuring Success and Optimizing for Local Search
- Frequently Asked Questions About Birdeye
- Can multiple team members use Birdeye at the same time
- What's the best login method for a franchise or multi-location business
- Why can someone log in but not see the right location
- Should front-line staff have admin rights
- How often should admins audit access
- Does Birdeye help local SEO
- What should a new user do after the first login
Why Your Birdeye Login Is Your Business's Front Door
At 8:15 a.m., a location manager is trying to answer a fresh one-star review before the lunch rush. The regional marketer needs to fix holiday hours for three branches. The owner is asking for a quick performance check. If one person is locked out, using the wrong login method, or waiting on a reset that never arrives, the delay hits customer-facing work first.
That is why Birdeye access deserves admin-level attention, especially for franchises and multi-location groups. Login settings decide who can respond to reviews, who can edit listings, who can see location data, and who can affect every storefront at once. For teams using Google SSO, Microsoft SSO, or MFA, access setup is part of operations, not a minor IT task.
Birdeye is used across local service categories and multi-location businesses. BuiltWith lists broad adoption in its Birdeye analytics, which helps explain why access management comes up so often during onboarding. If you are evaluating where the platform fits, this guide to Birdeye for review management and local reputation workflows gives the broader context.
Key Facts
- Login controls real business actions. A user session can lead to review replies, listing edits, inbox activity, or reporting access by location.
- Multi-location teams need tighter access rules. Store staff, practice managers, franchise owners, regional directors, and outside agencies should not share the same permissions.
- SSO and MFA reduce risk, but they also add failure points. A mismatched identity provider, expired invite, or incomplete MFA rollout can stall response time across several locations.
- Fast access supports faster reputation management. The speed of your team's response affects how quickly you can address complaints, confirm hours, and keep profiles current.
- One bad permission choice can spread across locations. Broad admin access is convenient at first and expensive later when the wrong user edits brand-wide settings.
Why access problems hurt conversions
Customers never see your internal login issue. They see the result. An unanswered complaint stays public. A closed holiday schedule remains wrong. A phone number routes to the wrong branch.
For a single-location business, that is frustrating. For a franchise or multi-location operator, it creates inconsistency that shows up market by market. One branch may have a trained manager with the right permissions, while another is relying on a shared inbox, an old employee login, or a broken SSO handoff. That gap slows response time and weakens trust right where prospects are comparing options.
The practical rule is simple. Treat Birdeye access as controlled operational access, with location-specific permissions and a clear owner for identity management.
I usually advise clients to decide three things early: who owns user provisioning, which login path the company supports, and which roles can affect one location versus all locations. Get those right first, and the rest of your Birdeye workflow gets easier to run.
How to Access Your Birdeye Account
The best birdeye login process is the one your team can repeat without thinking. If staff have to guess whether to use direct credentials, Google SSO, or an invite link, you'll get lockouts, duplicate users, and support tickets.
Birdeye supports a few common login paths. The right one depends on how your account was provisioned and whether your organization uses SSO (Single Sign-On) or MFA (Multi-Factor Authentication). If your primary goal is review operations after access is set, this overview of Birdeye review management is the next layer.
Direct login with email and password
Direct login works best for owner-operators, single practices, and smaller teams without centralized identity tools.
Go to Birdeye's login page and enter the email tied to your account. If you're new, use the invitation email your admin sent. If you're returning, use the same email that already has permissions assigned.
This path is usually the cleanest when one person manages one location or a small cluster. It also makes handoff easier when a practice manager needs to log in from a second device.
A few habits help:
- Use one business email per person. Shared inboxes create audit confusion later.
- Bookmark the correct login page. Teams often lose time because they start from an old invite or a stale browser tab.
- Confirm the assigned location access after login. Getting in isn't enough if the dashboard opens to the wrong business group.
Single Sign-On with Google Apple or Microsoft
SSO is usually the right fit for franchises, healthcare groups, and retailers with centralized IT. Instead of remembering a separate password, users authenticate through the identity provider the company already trusts.
Choose the provider button that matches your organization's setup, such as Google or Microsoft, then complete your standard business sign-in. If your company enforces conditional access or device rules, follow those prompts first.
The benefit is consistency. The trade-off is that login errors often come from identity sync, not Birdeye itself.
This walkthrough is helpful for teams that want to see the interface before rolling access out widely:
What to expect when MFA is enabled
MFA adds a second check after your password or SSO step. That might be a code, push prompt, or app verification depending on your company's security settings.
For admins, this is worth the extra step because review and listing tools control public-facing assets. For end users, the most important thing is consistency. Use the same method each time and make sure the device receiving codes is available during shift changes or travel days.
If a location manager can't complete MFA from the front desk, that isn't a security win. It's an operations problem.
Troubleshooting Common Birdeye Login Issues
It is 8:05 a.m., three location managers are trying to answer fresh reviews before opening, and one of them cannot get past login. In a single-location business, that is annoying. In a franchise or multi-location group, it can block responses, listing updates, and escalation workflows across the day.
The pattern is usually operational, not mysterious. A user signs in with the wrong email alias, an old browser session keeps forcing the wrong account, or the identity provider says the user is authenticated but Birdeye does not see the right location access attached yet. That distinction matters because the fix changes depending on whether the problem is local to the browser, tied to SSO, or caused by user provisioning.
If login trouble is happening at the same time your team is losing visibility or control over public profiles, treat that as a broader access problem. We see this spill into listing issues that later require a Google Business Profile suspension recovery process.
When the issue is browser cache or saved credentials
Start with the fastest test. Open a private or incognito window and sign in with the exact email that received the invite.
If that works, the browser is the problem. Clear cache and cookies for the site, remove any saved credentials that belong to former staff or alternate accounts, then retry. This comes up constantly at front desks, call centers, and shared workstations where multiple employees rotate through one machine and the browser keeps trying to be helpful.
A good admin habit is simple. Do not let shared devices store passwords for reputation platforms.
When SSO or MFA breaks the workflow
SSO failures usually come from identity mapping, not from the password screen itself. In franchise environments, I look at four things first. Was the user invited under the same email used in Microsoft or Google? Is the user in the correct directory group? Did the account sync recently? Is the user landing in Birdeye with no locations assigned and assuming login failed?
MFA failures have a different signature. The employee changed phones, the authenticator app was never reconnected, text codes are going to an old number, or the push prompt is blocked by device settings. Those are common after staffing changes, hardware swaps, or a rushed rollout across multiple stores.
Use this order to isolate the issue:
- Verify the exact email address. Matching the invited email to the SSO identity solves a surprising number of access tickets.
- Test in a private browser session. That removes stale cookies and expired tokens from the first round of troubleshooting.
- Check whether the user can authenticate but sees nothing useful. Successful sign-in with no assigned locations is a provisioning problem, not a password problem.
- Confirm the MFA method is still attached to the current device or number. Phone replacements break this more often than teams expect.
- Escalate to the person who manages your identity provider. Store managers rarely have the access needed to fix group membership, conditional access, or SSO app settings.
For reseller, partner, or layered admin setups, one extra check saves time. Confirm which team owns the identity configuration and which team owns Birdeye user provisioning. Multi-location brands often split those responsibilities, and tickets bounce around when no one names the system of record first.
When to escalate internally
Escalate quickly if the same user fails in multiple browsers, several users at one brand lose access at the same time, or a manager can sign in but cannot see assigned locations. Those are strong signs of a configuration issue upstream.
Access failures that hit multiple users at once usually point to SSO policy changes, expired provisioning, or role assignment errors.
Document three things before you hand it off. The email used to sign in, the exact error or screen shown, and whether the user reached the dashboard at all. That short record cuts down the usual back-and-forth and gets IT or your platform admin to the actual fix faster.
Admin Tips for Managing Team Access and Permissions
At a multi-location brand, access problems usually start after a user signs in. The login works, but the store manager cannot see their location, a regional operator has broader access than they should, or corporate is fielding tickets because one franchise group was set up differently from the rest.
That is an admin design problem. Birdeye access should mirror your operating structure, not just your org chart.
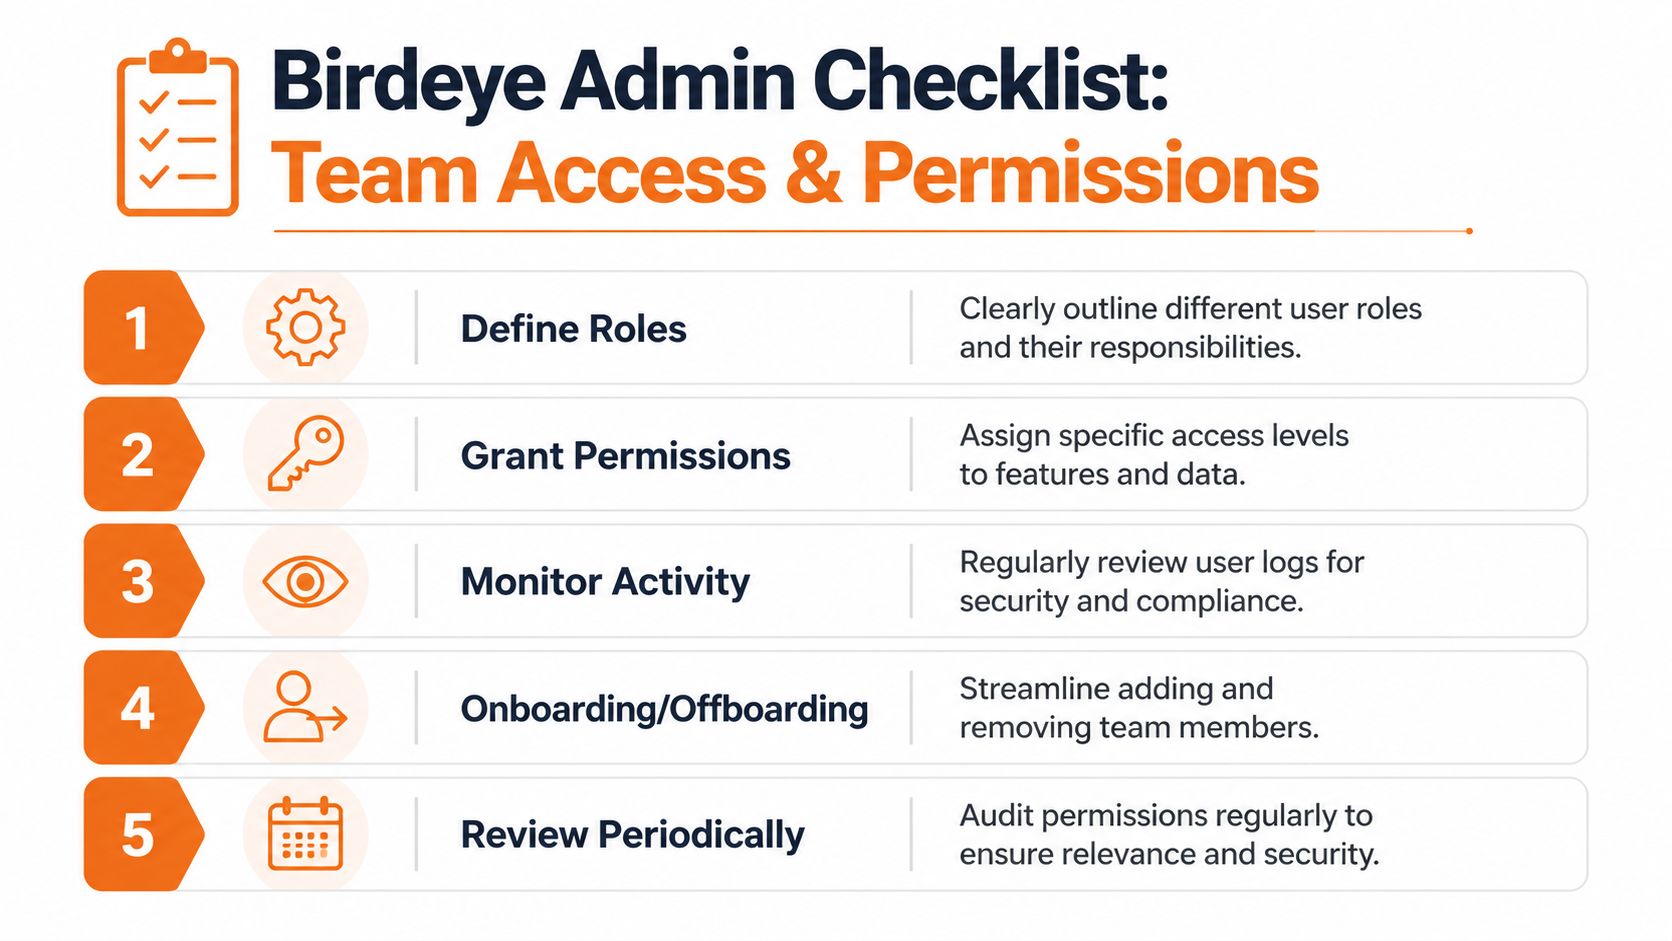
Birdeye support content on account settings and user management makes one thing clear. Permission mistakes and login-related configuration issues are common causes of wasted time for admins. In practice, I see the same pattern with franchise and multi-unit teams. The failure is rarely the password itself. It is usually the mix of role scope, location assignment, SSO group mapping, or MFA ownership.
If you have managed brand access elsewhere, the logic is similar to setting the right Facebook Page admin permissions for multi-user teams. Give each person enough access to do the job, and no more.
Set up roles before you invite users
Start with the work each person needs to do.
A front desk lead may only need review and message access for one location. A district manager may need visibility across ten stores without the ability to change account settings. A corporate marketing lead may need reporting, listings, and template oversight across the full brand. An IT owner or platform admin may need control over users, SSO-related coordination, and security settings.
For franchises, add one more layer before sending invites. Decide whether access is managed by brand, region, franchise group, or individual location. If that rule is fuzzy, users get assigned inconsistently, and every new opening creates cleanup work.
A simple permissions model that works
Use a short role list and apply it the same way across every market.
| Role | Best for | Should usually access |
|---|---|---|
| Location responder | Front desk, store manager | Reviews and messages for one location |
| Regional operator | Area manager, regional ops | Multiple locations, limited settings |
| Marketing admin | Corporate marketing | Reviews, listings, reporting |
| System admin | Owner, senior admin, IT lead | User management and account settings |
A few admin rules prevent most access drift:
- Keep super admin access limited. One primary owner and one backup is usually enough.
- Split platform administration from day-to-day response work. Review responders do not need account-wide control.
- Assign locations deliberately. A correct role with the wrong location group still creates risk.
- Offboard on the same day employment or agency access ends. Waiting until the end of the week is how former users stay active.
- Review access by franchise group or region every month. That is where inherited mistakes tend to hide.
Admin checks for SSO and MFA in multi-location accounts
This is the part generic setup guides skip.
If your company uses SSO, the Birdeye role plan needs to match the identity provider group structure. When those two systems are built separately, users authenticate successfully but land in the wrong scope or with no usable access at all. For franchise organizations, confirm who owns the source of truth. Some brands let corporate IT manage identity groups while field operations controls Birdeye provisioning. That split works only if both teams are using the same role map.
MFA needs ownership too. Decide whether users handle their own authenticator changes or whether your help desk resets them. Phone replacements, number changes, and shared location devices create more friction than admins expect. Document the reset path before rollout, especially for store-level users who need access at opening time.
7 day launch checklist for a review program
- Day 1. Define roles, location groups, franchise boundaries, and approval rules.
- Day 2. Add admin owners and confirm each account uses the correct business email.
- Day 3. Invite location users in controlled batches by region or franchise group.
- Day 4. Test access with one user per role type. Check login, MFA, assigned locations, and visible features.
- Day 5. Confirm who handles SSO group changes, MFA resets, and urgent access tickets.
- Day 6. Review listing edit rights, response permissions, and brand-level guardrails.
- Day 7. Audit active users, remove extras, and save a written access policy for future openings and staff changes.
Key Templates and Scripts to Use After You Log In
Access is only step one. Once you're in, the fastest path to value is to start a disciplined review request and response rhythm that front-line teams can maintain.
The strongest templates are short, location-aware, and easy to personalize. They also respect compliance. In healthcare, don't include PHI (Protected Health Information). In senior living or housing-related contexts, keep wording neutral and avoid steering language.
If your team needs a broader library, these customer service response templates can help standardize tone across locations.
SMS review request template for HVAC
This works because it respects the channel. SMS should feel like a quick follow-up, not a campaign.
Hi [First Name], thanks for choosing [Business Name] today for your HVAC service in [City]. If you have a minute, we'd appreciate your feedback here: [Review Link]. Thank you for your time.
Use this right after the visit while the experience is still fresh. Keep it plain. No pressure, no incentives, no extra links.
Email review request template for dental
Email can carry a little more context, especially for dental, med spa, vet, and auto service follow-up.
Subject: Thanks for visiting [Practice Name]
Hi [First Name],
Thank you for visiting [Practice Name] in [Neighborhood]. We appreciate the opportunity to care for you.
If you'd like to share feedback about your visit, you can leave a review here:
[Review Link]
Your feedback helps future patients find a provider they can trust.
Thank you,
[Practice Name]
This version works because it sounds professional without sounding scripted. It also avoids any reference to treatment details.
Review response templates
Positive review response
Hi [Name], thank you for the kind words about your experience with [Business Name]. We're glad our team could help. We appreciate you taking the time to share your feedback and look forward to serving you again in [City].
Negative review response
Hi [Name], thank you for sharing your feedback. We're sorry your experience didn't meet expectations. We take concerns like this seriously and want to learn more. Please contact us at [Phone/Email] so our team can review the situation directly.
The positive reply reinforces consistency and local trust. The negative reply does something more important. It acknowledges the concern without arguing in public.
Measuring Success and Optimizing for Local Search
The point of a smooth birdeye login isn't dashboard access. It's business outcomes. Once your team is logging in consistently and using the platform, you need to track whether review activity is improving local visibility and lead flow.
Birdeye's review request system has shown strong engagement. Review request emails achieved a 69% open rate and 22% click-through rate, and businesses using the system averaged 66 new Google reviews per location in a year, according to Birdeye's online reviews statistics. Those numbers matter because they connect outreach behavior to review momentum.
What to measure inside your workflow
For busy operators, keep the scorecard tight:
- Review volume. Are locations generating fresh reviews consistently each month
- Recency. Did this location get recent reviews, or is the profile stale
- Response time. Are negative reviews being answered quickly
- Star rating. Is the rating stable and credible over time
- GBP views and actions. Track views, calls, website clicks, bookings, and direction requests from your Google Business Profile
- Lead-to-sale conversion. Compare leads from GBP with closed jobs, appointments, or tours
If one location gets reviews but doesn't convert, the issue may be intake, scheduling, or the landing experience. Reviews help attract attention, but operations close the loop.
How Google decides who shows up near me
Google's local model is usually explained through proximity, relevance, and prominence.
- Proximity means how close the searcher is to your location.
- Relevance means how well your profile matches the search intent.
- Prominence reflects trust signals such as reviews, brand visibility, and profile completeness.
For a search like “vet near me” in [Neighborhood], proximity matters a lot. For “best dentist in [City],” relevance and prominence play a bigger role. That's why accurate categories, service details, recent reviews, and review responses all matter together.
A complete profile with fresh reviews gives Google more confidence about what your location does and whether customers trust it.
Google Business Profile checklist and UTM tracking
Use this short Google Business Profile checklist:
- Primary category is correct
- Hours are current
- Phone and website match your location
- Services are filled out clearly
- Photos are recent
- Review responses are active
- Booking or appointment links work
- Location description mentions real services and city terms naturally
For tracking, add UTM parameters to the website link on your GBP. That lets you separate Google Business Profile traffic inside analytics and follow the path from profile view to call or booking request. Keep naming consistent by location so your reporting doesn't become a cleanup project later.
Frequently Asked Questions About Birdeye
Can multiple team members use Birdeye at the same time
Yes, but they shouldn't share one login. Give each user their own account and assign access by role and location.
What's the best login method for a franchise or multi-location business
SSO is usually the cleanest option when corporate IT manages identity centrally. Smaller groups often do fine with direct login if permissions are organized well.
Why can someone log in but not see the right location
That usually points to a permissions issue, not a failed login. Check the assigned location group and user role first.
Should front-line staff have admin rights
Usually no. Most front-line users only need access to reviews, messages, or limited location functions.
How often should admins audit access
Do it on a regular operating cadence and any time staff, agencies, or regional responsibilities change. Offboarding should happen immediately.
Does Birdeye help local SEO
It supports local SEO by making review generation, review response, and listing management easier to run consistently. That consistency strengthens relevance and prominence signals.
What should a new user do after the first login
Confirm the correct location, test the review request flow, review templates, and make sure alerts route to the right person. That gets the account from “accessible” to “usable.”
If you want help turning Birdeye access, review workflows, and Google Business Profile management into a system your locations can successfully maintain, Reviews To The Top offers month-to-month support with a single point of contact. If you'd like a practical next step, you can book a strategy call and map out the right setup for your locations.


